Harika! Yazıyı İngilizce olarak, teknik terimlere sadık kalarak ve akıcı bir blog formatında senin için hazırladım: Web Server Rec...
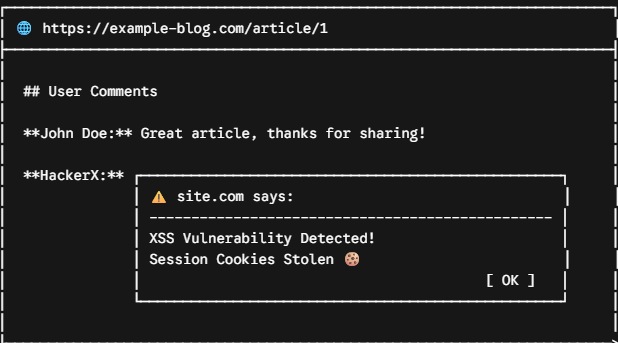
Demystifying Cross-Site Scripting (XSS): From Injection Mechanics to Advanced Filter Evasion Cross-Site Scripting (XSS) remains on...
Actually, it all goes back to my childhood dream. When I started school and my teacher asked, 'What do you want to be when you gro...
Mastering Web Application Content Discovery: A Pentester’s Workflow When conducting a web application penetration test, finding hi...
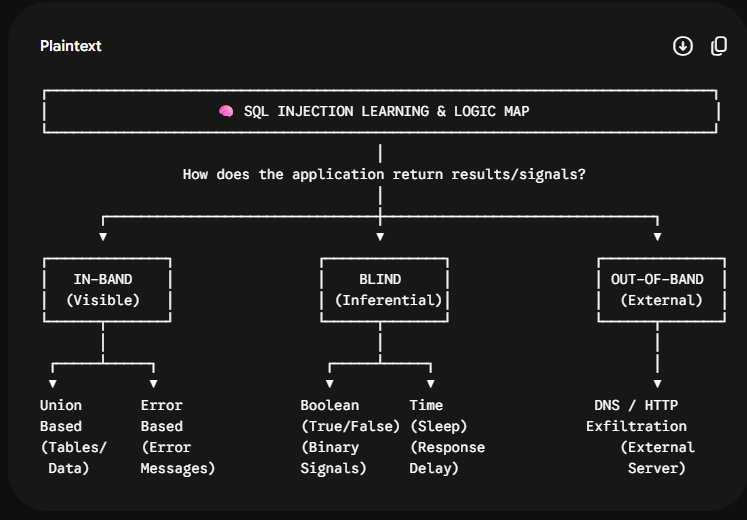
Mastering SQL Injection: From Union-Based Extraction to Time-Based Blind Attacks In our previous post, we explored IIS enumeration...
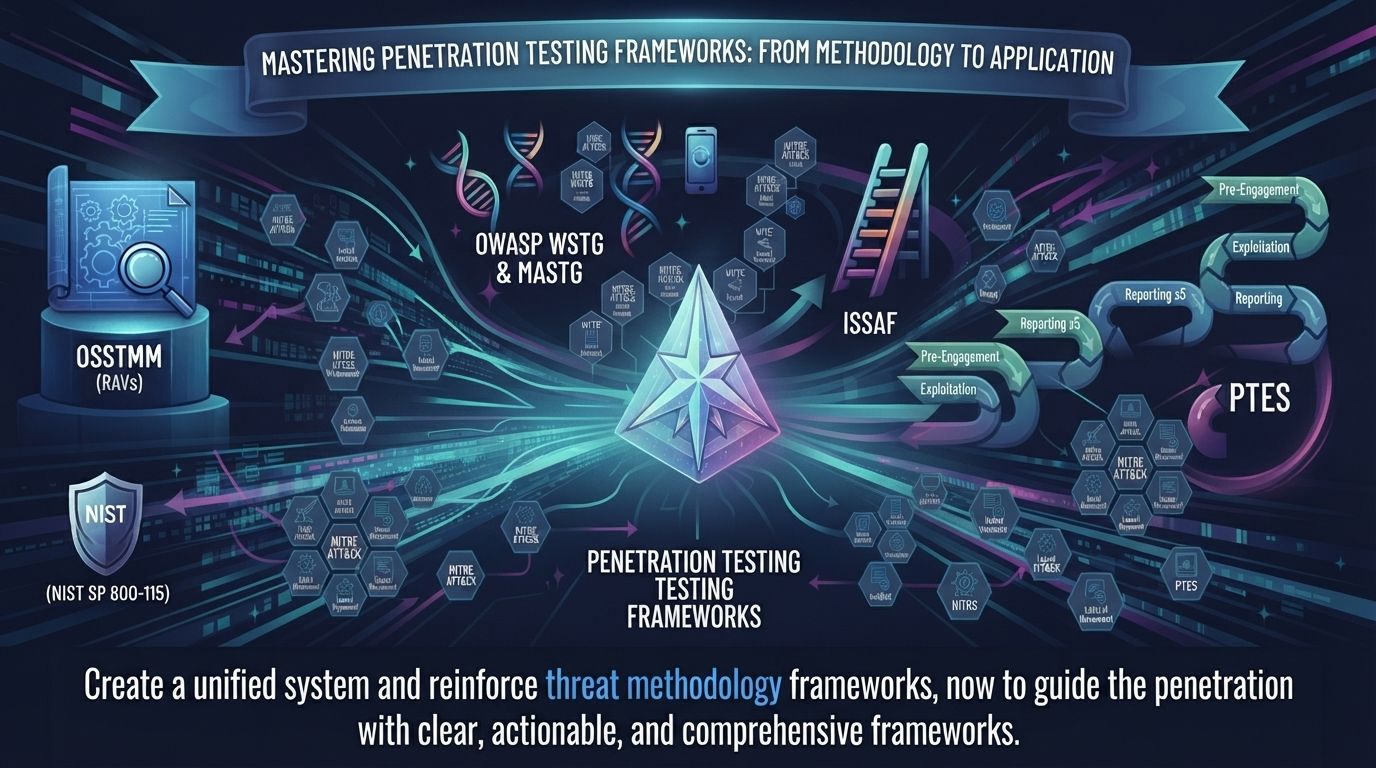
Mastering Penetration Testing Frameworks: A Comprehensive Guide for Junior Pentesters Navigating the cybersecurity landscape requi...
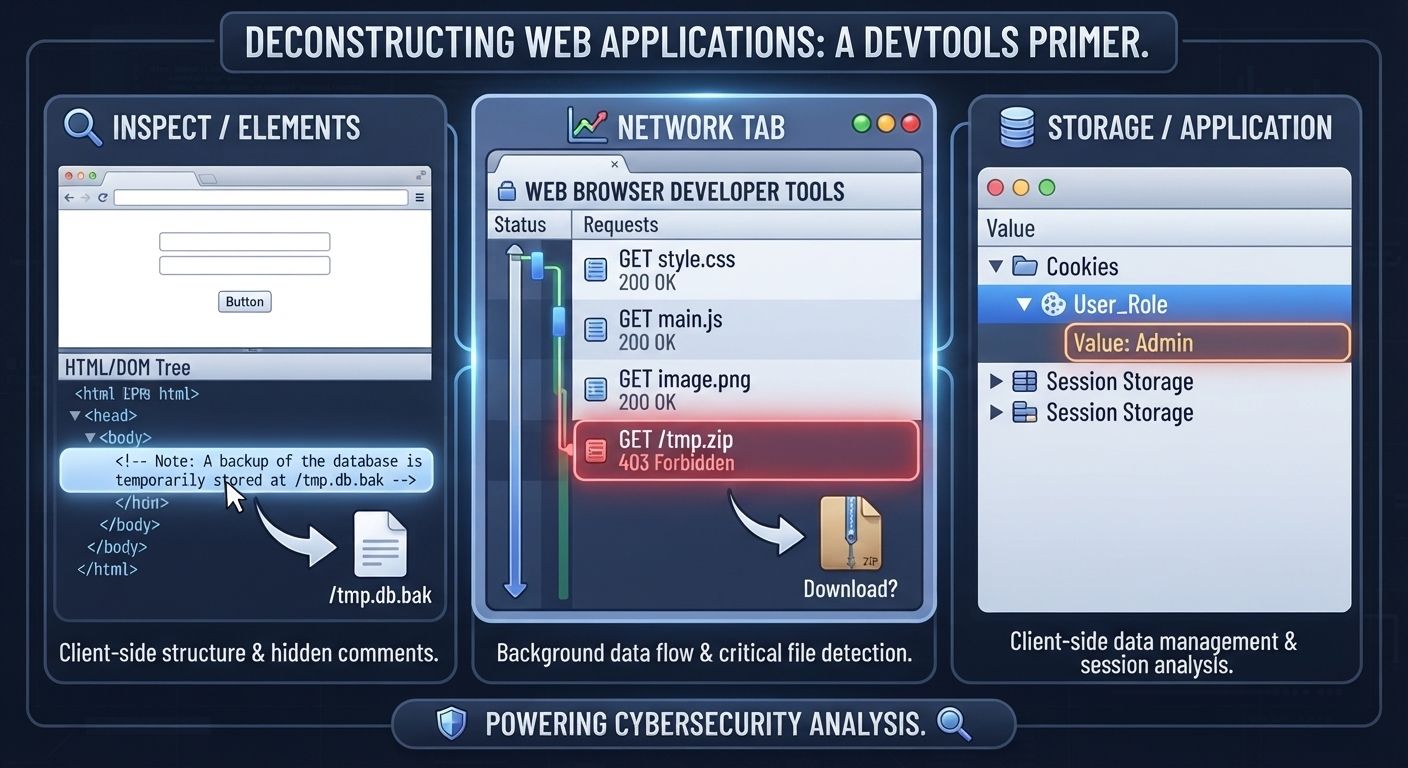
A Guide to Developer Tools (DevTools) in Web Application Analysis In the worlds of web development and cybersecurity, built-in bro...
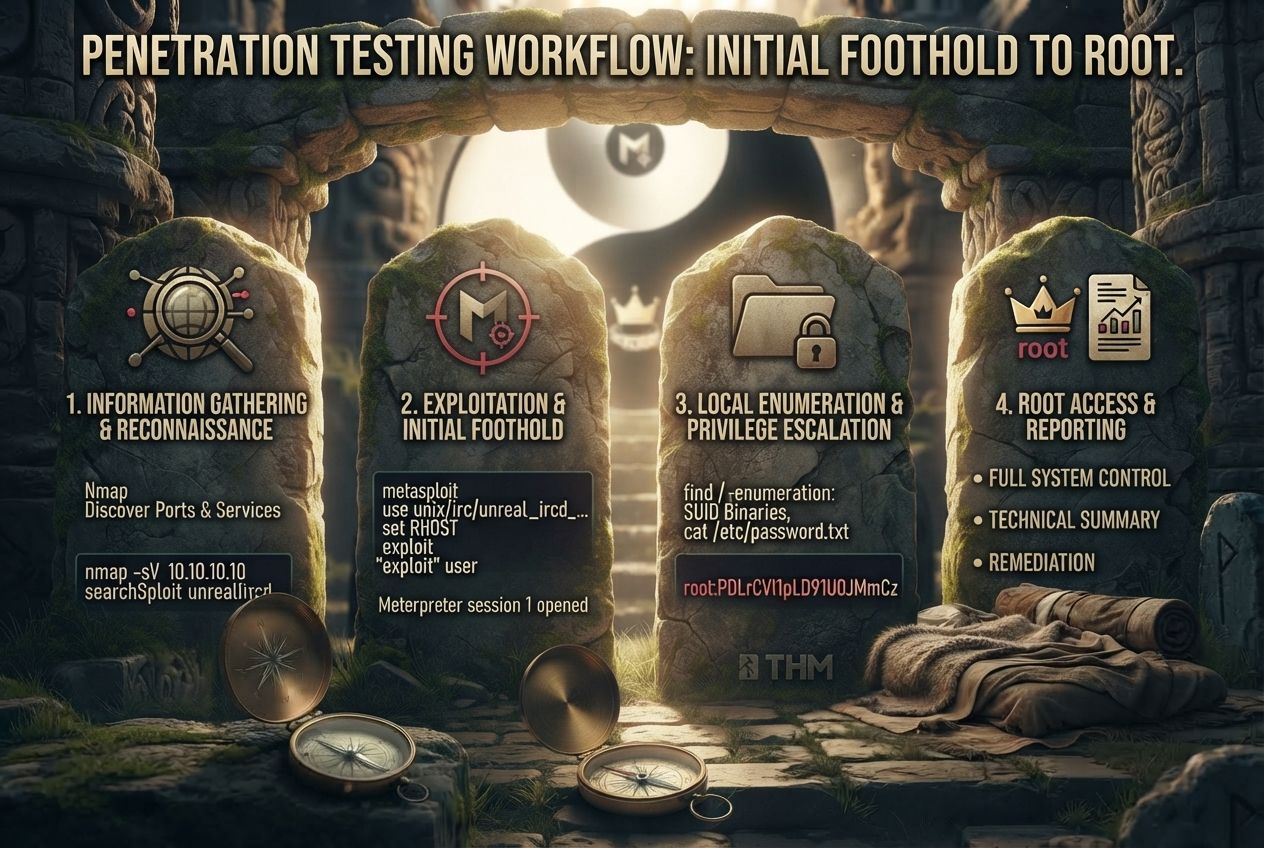
In this walkthrough, we will break down a complete penetration testing workflow—from initial reconnaissance and service enumeratio...
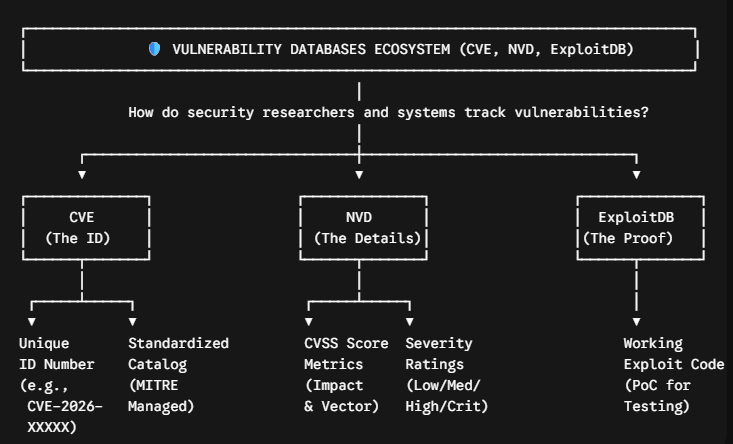
Demystifying Vulnerability Databases: A Guide to CVE, NVD, and ExploitDB In the fast-paced world of cybersecurity, new software fl...
Modern web penetration testing often shifts from black-box guessing to targeted, evidence-driven exploitation. Different technolog...
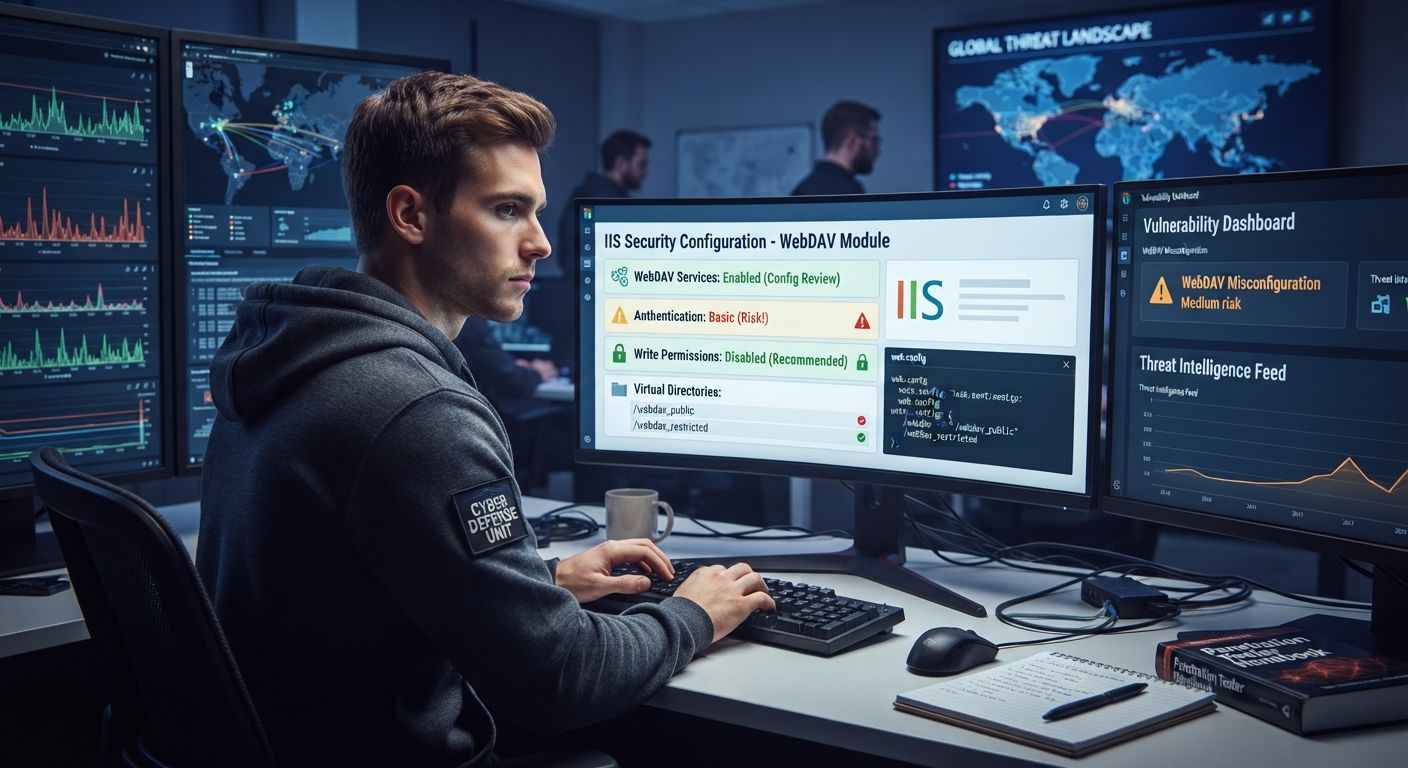
Hardening, Enumeration, and Privilege Escalation: A Guide to IIS Security Assessments In this post, we cover the core methodology ...
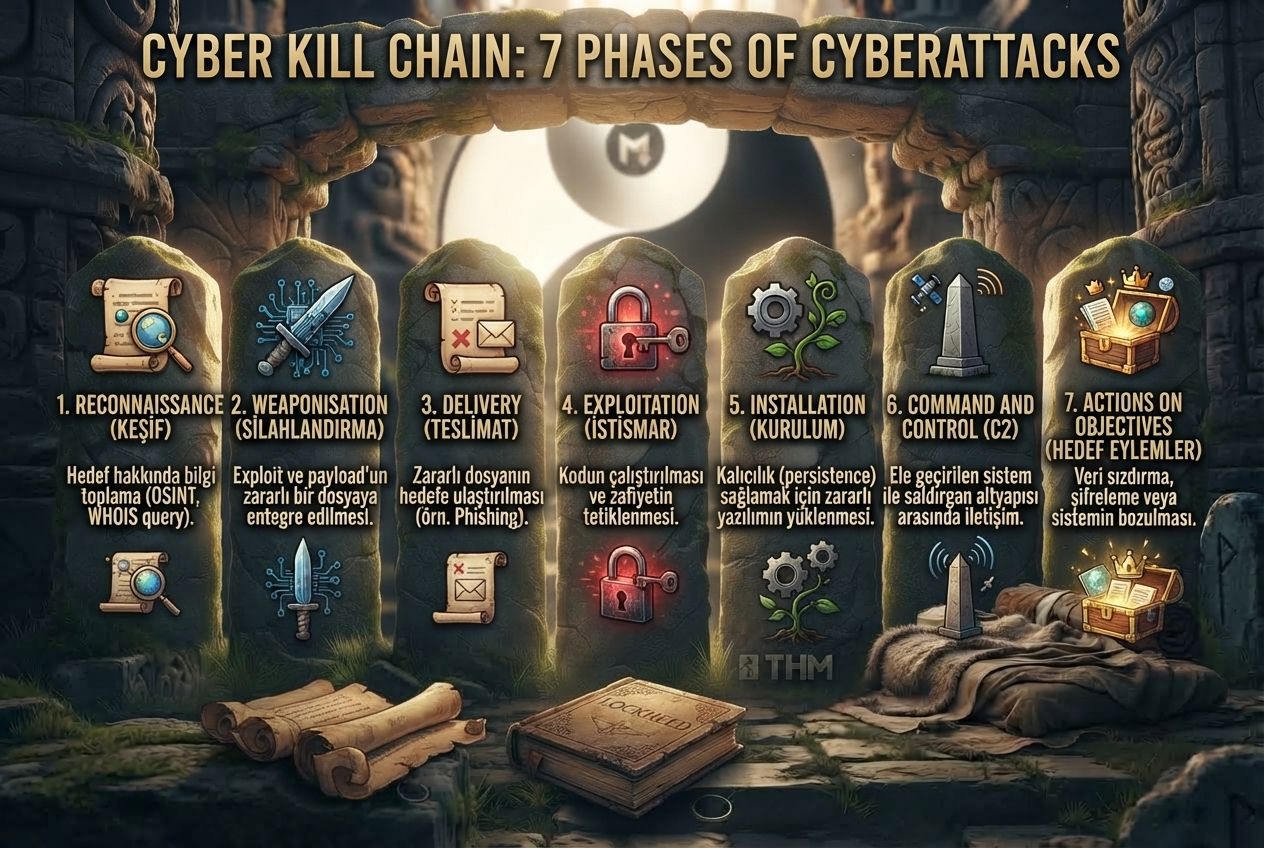
Mastering the Cyber Kill Chain: A Blueprint for Offense and Defense Understanding how adversaries operate is the foundation of mod...
Mastering Metasploit: A Practical Guide for Beginners When you land on a penetration testing engagement—say, auditing a mid-sized ...